

AI Summarize


Share


A GDPR Cookies Policy is a document that discloses the cookies and tracking technologies a website uses, along with their purposes and lifespans, as required by the General Data Protection Regulation (GDPR) and the ePrivacy Directive.
Any website that targets users in the European Union and sets non-essential cookies needs to provide relevant information about its cookie practices, and a dedicated Cookies Policy is the clearest way to do so.
Cookie Policies notably support transparency requirements and informed consent under the GDPR, and failing to uphold those principles carries consequences. Regulators across the EU enforce cookie consent rules, with maximum GDPR fines reaching up to €20 million or 4% of global annual turnover, whichever is higher.
This article explains what a GDPR Cookies Policy is, the law behind it, which cookies need consent, and how to implement a compliant Cookie Policy in practice. In addition, we go over Cookie Policy contents, a usable template, cookie audits, US and global compliance angles, enforcement, and frequently asked questions.
Creating a Cookies Policy from scratch is time-consuming and error-prone, which is why platforms like TermsFeed offer a Cookies Policy generator that creates a tailored, GDPR-ready document in minutes.
Our Cookies Policy Generator can create a custom and professional Cookies Policy for your website.
-
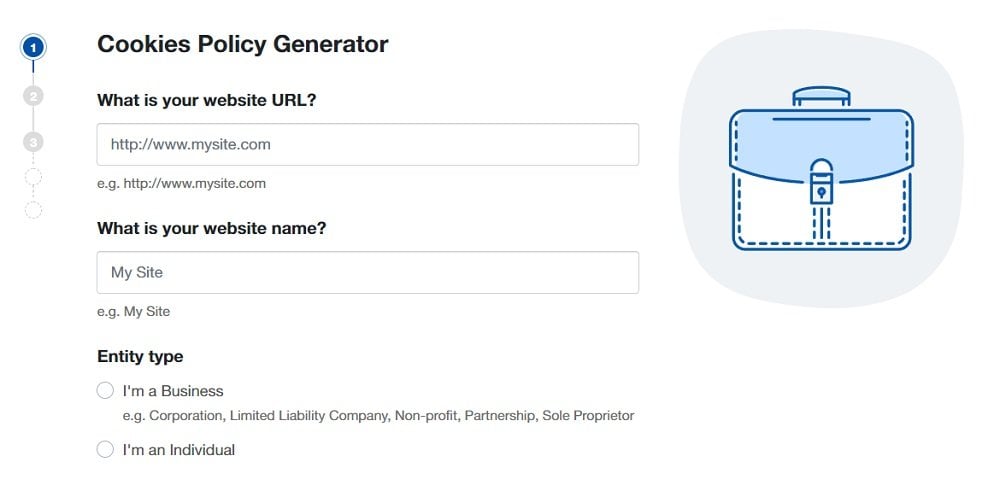
At Step 1, add in information about your website.
-
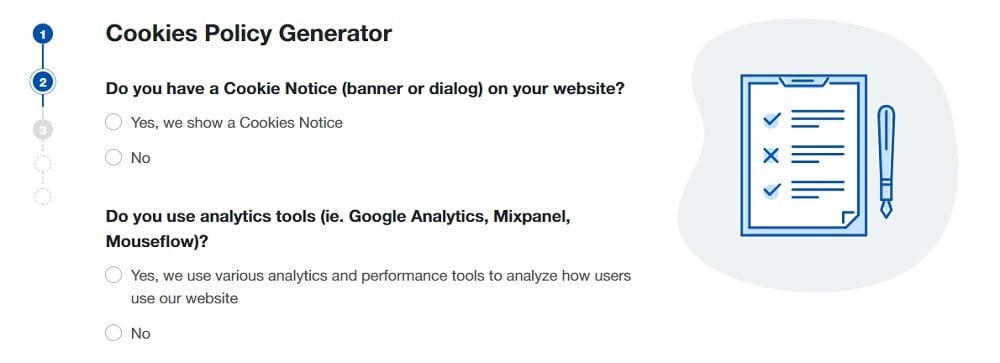
Answer some questions about your business.
-
Enter an email address where you'd like to receive your Cookies Policy and click "Generate."
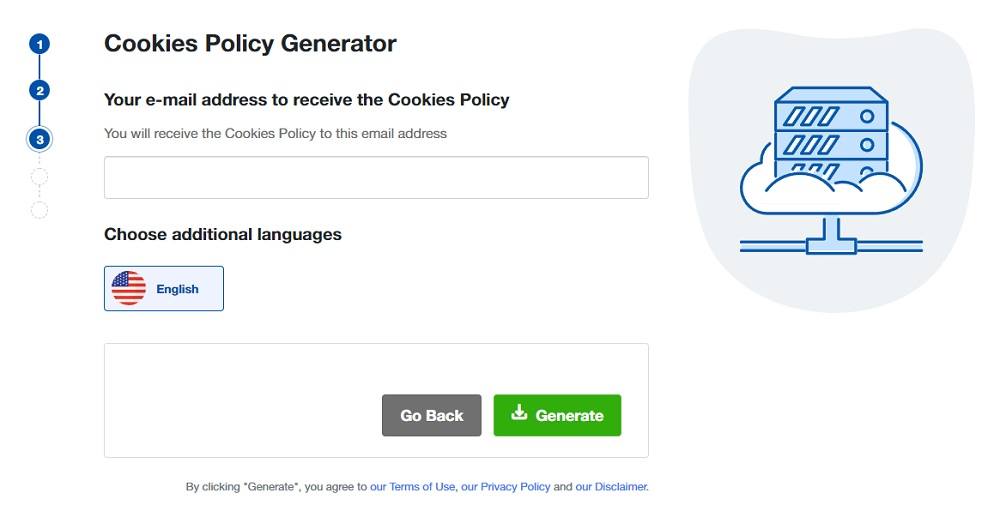
Done! You'll be able to instantly access and download your new Cookies Policy.


- 1. What Is a GDPR Cookies Policy?
- 2. Cookies, the GDPR, and the ePrivacy Directive
- 2.1. What is the ePrivacy Regulation?
- 3. Are Cookies Personal Data Under the GDPR?
- 3.1. Anonymized vs. Pseudonymized Data
- 4. Types of Cookies Under the GDPR
- 5. Does the GDPR Require Consent for All Cookies?
- 5.1. Cookies That Don't Require Consent
- 5.2. Cookies That Require Consent
- 6. GDPR Cookie Consent Requirements
- 6.1. Freely Given, Specific, and Informed Consent
- 6.2. Consent via a Clear, Affirmative Act (No Pre-Ticked Boxes)
- 6.3. Easily Withdrawn Consent
- 6.4. Records of Consent
- 7. How to Implement GDPR Cookie Consent (Step-by-Step)
- 7.1. Show a Cookie Consent Banner on First Visit
- 7.2. Block Non-Essential Cookies Before Consent
- 7.3. Let Users Manage and Withdraw Consent Anytime
- 7.4. List the Cookies You Use
- 7.5. Register and Store Consent Records
- 8. Do You Need a GDPR Cookies Policy?
- 8.1. Cookies Policy vs. Cookie Notice
- 8.2. Cookies Policy vs. Privacy Policy (or Both?)
- 9. What to Include in a GDPR Cookies Policy
- 10. How to Create a GDPR Cookies Policy
- 11. GDPR Cookies Policy Template
- 12. Cookie Compliance Beyond the EU
- 12.1. CCPA and CPRA Cookie Compliance
- 12.2. Other Cookie Laws (ePrivacy/PECR, PIPEDA, LGPD)
- 13. Google Consent Mode and GDPR Cookies
- 14. How to Audit Your Cookies for GDPR Compliance
- 15. GDPR Cookie Consent Fines and Penalties
- 16. GDPR Cookies Policy: Frequently Asked Questions
- 17. Summary and Key Takeaways
What Is a GDPR Cookies Policy?
A GDPR Cookies Policy is a legal document that explains how a website uses cookies and similar technologies in ways that comply with the GDPR and ePrivacy Directive. It outlines the cookies and trackers a site uses, explains their purposes and lifespans, identifies relevant third parties, and tells users how to give, decline, and withdraw consent.
Cookie Policies are sometimes conflated with two related legal agreements: the Cookie Notice and the Privacy Policy. A Cookie Notice is the banner or pop-up that prompts visitors to accept or reject cookies, while a Cookies Policy is the reference document that explains the details behind those choices.
A Privacy Policy, however, is a broader legal document that explains how a business collects, processes, shares, retains, and protects personal data (i.e., any information reasonably able to identify a person). Privacy Policies often address cookies as well, but usually in less operational detail than a standalone Cookies Policy.
Applicable websites use all 3 legal agreements for different compliance functions. Below is a quick breakdown of their differences.
| Document | What It Does | Where Users See It |
| Cookie Notice | Presents the user interface (banner or pop-up) on the first site visit of a user and asks for consent to load non-essential cookies | Pop-up or banner when a webpage loads |
| Cookies Policy | Comprehensively explains the cookies and similar trackers a website uses, along with their purposes, duration, and user controls | Linked page, usually in the Cookie Notice and website footer |
| Privacy Policy | Clarifies broader personal-data handling practices, including cookies and trackers that contain personal data | Linked page, usually in the Cookie Notice and website footer |
The requirement for a Cookies Policy comes from two overlapping legal frameworks. Article 5(3) of the ePrivacy Directive requires websites to provide "clear and comprehensive information” about cookies and obtain consent before storing or accessing information (including cookies) on the devices of visitors.

The GDPR applies when the information involved qualifies as personal data under Article 4(1) of the GDPR. The GDPR defines personal data broadly as any information relating to an identified or identifiable person.

A Cookies Policy exists because businesses need a dedicated legal document that meets the overlapping requirements of both the GDPR and ePrivacy Directive.
Any website that targets users in the European Union and sets non-essential cookies therefore needs a GDPR Cookies Policy (either as a standalone document or well codified in a Privacy Policy). This obligation applies regardless of where your business is based, as long as you offer goods or services to people in the EU or monitor their behavior.
Cookies, the GDPR, and the ePrivacy Directive
Cookie rules across the EU come from two laws working together.
- Directive 2002/58/EC (ePrivacy Directive, often called the EU Cookie Law)
- Regulation (EU) 2016/679 (known as the General Data Protection Regulation or GDPR)
The ePrivacy Directive sets the rules governing cookie consent, including requiring businesses to provide clear information and obtain consent before storing information on user devices or accessing information already stored there. Strictly necessary cookies and transmissions over an electronic communications network are the only exception to the consent requirements.
The GDPR regulates everything that happens once information qualifies as personal data. Cookies only become personal data when the information they store or access on user devices relates to an identified or identifiable person, either directly or indirectly.
Under Article 95 of the GDPR, this is a relationship called lex specialis: the more specific law applies first, and the general law fills any remaining gaps. Put simply, the ePrivacy Directive takes precedence over the GDPR when it comes to cookie consent.
The legal hierarchy here matters because Article 6(1) of the GDPR sets out six lawful bases for processing personal data. They include consent, contractual obligation, legal obligation, vital interests, public interest, and legitimate interests.

So while the GDPR lets businesses process personal data under five other lawful bases besides consent, that provision does not override consent requirements under the ePrivacy Directive when using non-essential cookies.
In other words, consent is mandatory for non-essential cookies, regardless of which GDPR lawful basis your business uses to process personal data.
A common misconception holds that the GDPR repealed the ePrivacy Directive when it took effect in 2018. It did not. The GDPR replaced the older 1995 Data Protection Directive, not the ePrivacy Directive. The GDPR and ePrivacy Directive have operated side by side ever since.
What is the ePrivacy Regulation?
The ePrivacy Regulation is a broader electronic communications privacy law meant to replace the ePrivacy Directive. However, the regulation no longer exists in its previous form.
The European Commission first proposed the ePrivacy Regulation to replace the ePrivacy Directive in 2017. After years of Council deadlock, the Commission announced the withdrawal in February 2025 and formally withdrew the proposal in October 2025.
In its place, the Commission published the Digital Omnibus Regulation Proposal in November 2025, which proposes folding cookie consent directly into the GDPR through two new articles.
- Article 88a restructures how consent for accessing a device works, effectively taking over the role Article 5(3) of the ePrivacy Directive plays today.
- Article 88b makes browser-level consent signals (a setting a user configures once) legally binding on every site the browser visits.
Neither provision is law yet. Both are working through the ordinary EU legislative procedure. Until that process concludes, businesses stay compliant by treating the cookie consent requirements under Article 5(3) of the ePrivacy Directive as the operative rule.
Are Cookies Personal Data Under the GDPR?
Yes, when a cookie can be linked to an identified or identifiable person, the information associated with that cookie qualifies as personal data under Article 4(1) of the GDPR.
Recital 30 of the GDPR backs this up by specifically naming cookie identifiers and Internet Protocol (IP) addresses as online identifiers that leave traces and, when combined with other information, help create profiles or identify individuals.

In addition, the European Commission lists cookie IDs among examples of personal data. This understanding was confirmed in the landmark Breyer judgment (Case C-582/14).
The Court of Justice of the European Union (CJEU) ruled that a dynamic IP address counts as personal data to websites if there is any legal or practical route (even through a third party like an internet provider) to connect it back to a person. The same logic applies to cookies.
That said, not every cookie is associated with personal data. On its own, a cookie identifier does not reveal the name or other information relating to a person. It only qualifies as personal data if the website or another party is able to use the cookie ID to single out or recognize someone when combined with other identifiers.
Once a cookie meets this bar, the legal requirements under the GDPR apply. This means your website must do the following.
- Comply with the consent standards under the GDPR
- Identify at least one lawful basis to process data
- Provide clear and comprehensive information about your data processing practices
- Help users exercise their GDPR privacy rights over their data
- Observe the GDPR privacy principles when processing data
Anonymized vs. Pseudonymized Data
At this point, it’s important to understand the concepts of pseudonymized and anonymized data. Pseudonymization changes personal data so it no longer directly identifies someone without additional details, but the data remains personal data under the GDPR.
Anonymization, however, involves changing the data so thoroughly that reversing or linking it back to a person is not possible by any means reasonably likely to be used. For this reason, properly anonymized data falls outside the coverage of the GDPR entirely.
The takeaway for businesses is to treat non-essential cookies as personal data until you can prove otherwise. Document your reasoning for any cookie classified as fully anonymized. Your classification determines the disclosures your Cookies Policy must include.
Types of Cookies Under the GDPR
Not all cookies are treated the same under the GDPR. Data privacy regulators and consent platforms widely sort cookies into 4 primary categories based on what each cookie does.
The key distinction for consent requirements is whether a cookie is technically necessary for the service a user requested or serves an additional purpose, such as remembering preferences or building ad profiles. The latter cookie categories generally require prior consent.
| Type | Purpose | Example | Consent Required? |
| Strictly Necessary/Essential | Enables core site functions and security | Login session, shopping cart | NO |
| Preference/Functionality | Remembers choices made by the user | Language selection, regional settings, UI themes. | YES |
| Analytics/Performance | Measures site usage and performance | Google Analytics 4 (GA4) | YES (unless fully anonymized) |
| Marketing/Targeting | Tracks activity for advertising or retargeting | Advertising pixels | YES |
This framework gives businesses a starting point for identifying cookie types and deciding which GDPR cookie categories need consent. That said, you still need a cookie audit to examine each cookie category individually and document their purpose, provider, duration, and data involved in your Cookies Policy.
Does the GDPR Require Consent for All Cookies?
No, only non-essential cookies need consent under the GDPR and ePrivacy Directive. Essential or strictly necessary cookies are exempt from consent obligations because they are required to provide a service the user requested, such as maintaining a login session or keeping items in a shopping cart.
Analytics, marketing, and other non-essential cookies generally require opt-in consent under the ePrivacy Directive before deployment. The GDPR applies only to cookies that collect or are associated with personal data.
The takeaway is to classify every cookie carefully and obtain consent for non-essential cookies before setting them on devices. Misclassifying an analytics cookie as strictly necessary, for instance, exposes your business to investigations and enforcement actions from data protection authorities.
Cookies That Don't Require Consent
Article 5(3) of the ePrivacy Directive provides 2 key exemptions from the cookie consent requirement: the communication exemption and the strictly necessary exemption.
- The communication exemption covers cookie storage or access used solely to transmit a communication across an electronic communications network. A load-balancing cookie that directs requests between servers, for example, falls within this exemption when its sole function is to support that transmission.
-
The strictly necessary exemption covers cookies required to provide an information society service that the user explicitly requested. Common examples include the following.
- Authentication and session cookies: Maintain a logged-in session while the user navigates the site.
- Shopping cart cookies: Keep selected products associated with a user during checkout.
- Security cookies: Detect fraudulent activity or protect an account from unauthorized access.
- Cashback or reward cookies: Attribute a transaction to a reward service or loyalty program the user specifically requested, where that attribution is necessary to provide the service. Some affiliate cookies fall under this exemption.
These exemptions are very narrow. A cookie that improves convenience or remembers user preferences does not qualify solely because it benefits the user. Each cookie requires an assessment of its actual function.
In short, cookies that do not require consent must pass one primary test: does the feature explicitly requested by a visitor work without those cookies? If not, the cookie is strictly necessary. Login sessions, shopping carts, and fraud checks all meet that standard.
Cookies That Require Consent
Cookies that fall outside the 2 narrow exemptions in Article 5(3) of the ePrivacy Directive require prior consent before being stored on user devices. This generally includes the following.
- Analytics cookies: Track or measure visitor behavior on a website to improve site performance and user experience.
- Advertising cookies: Support personalized advertising and ad measurement.
- Retargeting cookies: Follow users across sites or services for marketing purposes.
- Social media trackers: Transmit information to social platforms through embedded features or plugins.
- Third-party tracking technologies: Collect or access information for purposes unrelated to providing the service requested by the user.
Non-essential cookies and tracking scripts need to remain blocked until the user provides consent. Loading cookies first and displaying a consent banner afterward does not satisfy the requirement. Guidance from the European Data Protection Board (EDPB) emphasizes the need for technical measures that prevent cookies from transmitting data before consent.
Cookies that have been properly anonymized are exempt from GDPR obligations altogether, but this does not necessarily exempt them from the consent requirements of the ePrivacy Directive. Businesses still need to obtain consent before storing or accessing anonymized information on user devices unless the information is strictly necessary or used solely for communication.
GDPR Cookie Consent Requirements
The GDPR sets a high bar for valid cookie consent. Under Article 4 (11), consent must meet these standards.
- Freely given
- Specific
- Informed
- Unambiguous
- Expressed through a clear, affirmative act
Together, these requirements form the GDPR standard for consent, as shown below.

Article 7 of the GDPR further expands on the conditions for valid consent, noting that controllers must be able to show proof of consent with clear records and that consent must be just as easy to withdraw as it was to give.

By these same standards, cookie walls (i.e., website pop-ups or banners that block access to content unless a visitor agrees to accept cookies) and pre-ticked checkboxes, which place cookies on devices by default, both fail the standards for valid consent under the GDPR.
Under Recital 25 of the ePrivacy Directive, "users should have the opportunity to refuse to have a cookie or similar device stored on their terminal equipment." This means that you need to get consent before you use most cookies.
When the EU says "consent," it really means it. Some privacy laws, such as CAN-SPAM in the United States, allow businesses to assume that they have user consent unless they opt out. The GDPR does not allow "opt-out"consent. It operates on a strict "opt-in"consent model.
Similarly, some privacy laws, such as the Canadian Anti-Spam Law, allow businesses to infer that they have a person's "implied" consent. For example, if they have an existing business relationship with that person. The GDPR does not recognize implied consent. It only recognizes "express" consent.
Most websites request cookie consent via a pop-up banner or landing page. You must build facilities into your website that allow your users to accept, refuse, and withdraw consent for different types of cookies.
Regulators enforce these requirements actively, as the French data protection authority (CNIL) demonstrated by fining Google €150 million and Facebook €60 million in January 2022 for making cookie rejection harder than acceptance.
Freely Given, Specific, and Informed Consent
Valid consent starts with a genuine choice where users understand what they are accepting and are free to refuse at any time. This requires first meeting the 3 conditions below.
- Freely given: Access to a service cannot depend on accepting non-essential cookies. A cookie wall that blocks a site until a user accepts tracking fails this condition.
- Specific: Consent needs sufficient granularity for the purposes involved. A single "Accept all" choice that bundles analytics, advertising, and other unrelated purposes does not provide the same level of choice as separate controls for each purpose.
- Informed: Users need clear, plain-language information before giving consent, including what data you collect and process, why you process it, and which third parties you share data with (where relevant).
These conditions work together. An aesthetically pleasing banner design does not make forced or bundled consent valid. Users need enough information to agree and an easy, meaningful way to refuse.
Consent via a Clear, Affirmative Act (No Pre-Ticked Boxes)
Valid consent requires a clear affirmative act that shows an unmistakable choice to agree, such as ticking an empty checkbox or clicking an "Accept” button with an explanation of your choices.

Inactivity and scrolling do not qualify as consent under the GDPR. The Court of Justice of the European Union confirmed this in Planet49 (Case C-673/17), ruling that only active behavior like ticking an empty checkbox constitutes valid cookie consent.
The European Data Protection Board (EDPB) backs this up in Guidelines 05/2020, stating that scrolling or swiping does not clearly communicate agreement since it is impossible to tell whether the visitor agreed or simply overlooked the cookie banner.
To comply with these requirements, your cookie banner needs to set every non-essential cookie toggle to off by default. Users must confirm their agreement to cookies and similar trackers with a deliberate action.
Easily Withdrawn Consent
Article 7(3) of the GDPR mandates that withdrawing consent must be as simple for users as granting it.
Website owners must provide a persistent, easily accessible mechanism (such as a sticky "Cookie Preferences" icon or website footer link) that allows visitors to change or revoke their choices at any time. For example, OpenAI uses a website footer link that lets users manage cookies.

Once you click the link, you have access to the same cookie categories you originally accepted and simply toggle them off to change your choices.

All non-essential tracking scripts must immediately stop loading when a visitor withdraws consent, and existing non-essential cookies must be rendered inactive. In addition, refusing tracking must not degrade user experience or block access to site content.
The rest of the site must remain available without penalizing the user for changing their decision, so their choices remain free and uncoerced.
These requirements are actively enforced by data protection authorities. Case in point, the French data protection authority (CNIL) fined Orange €50 million in 2024 for continuing to read cookies after users withdrew consent. The company later demonstrated compliance by removing first-party cookies with a script and stopping requests to third-party domains.
Records of Consent
Article 7(1) of the GDPR requires businesses that rely on consent to prove that they obtained valid consent. The law does not prescribe one fixed consent logging format, but a useful audit trail needs enough detail to reconstruct the choice made at the time.
For cookie consent, useful records of consent typically document the following.
- The visitor or session identifier (a consent ID or pseudonymous cookie ID)
- The date and time of the choice
- The cookie categories accepted or refused
- The version of the banner and the Cookie Policy shown
- The method of consent (button click, toggle switch)
Subsequent changes or consent withdrawals belong in the same consent log history. A detailed log is the only evidence of valid consent during an audit or privacy dispute, and a business without it fails to prove its compliance even when the consent was genuine.
How to Implement GDPR Cookie Consent (Step-by-Step)
Here's how to put compliant cookie consent into practice, in 5 steps that follow the order a visitor experiences them. One fundamental principle to observe for cookie consent implementation: no non-essential cookie or script loads before consent.
Use our Cookie Consent all-in-one solution (Privacy Consent) for cookies management to comply with GDPR & CCPA/CPRA and other privacy laws:
- For GDPR, CCPA/CPRA and other privacy laws
- Apply privacy requirements based on user location
- Get consent prior to third-party scripts loading
- Works for desktop, tables and mobile devices
- Customize the appearance to match your brand style
Create your Cookie Consent banner today to comply with GDPR, CCPA/CPRA and other privacy laws:
-
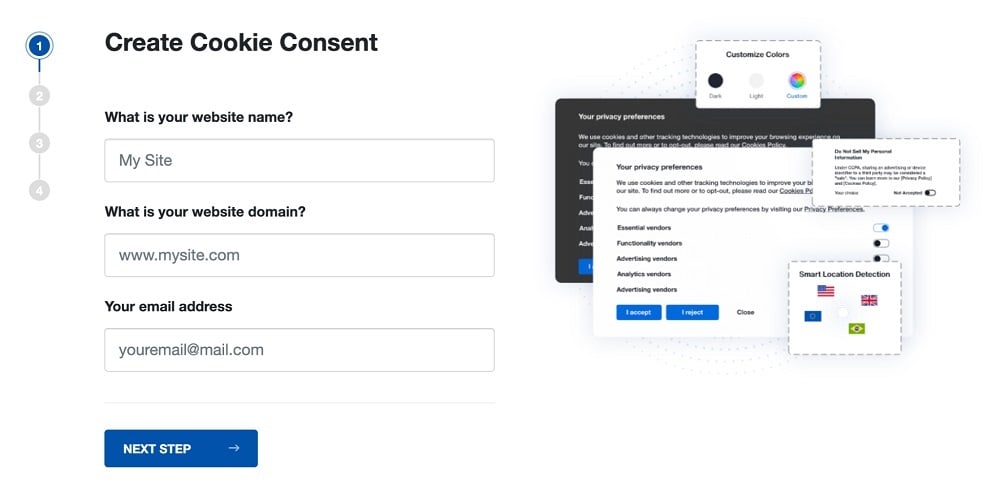
Start the Privacy Consent wizard to create the Cookie Consent code by adding your website information.
-
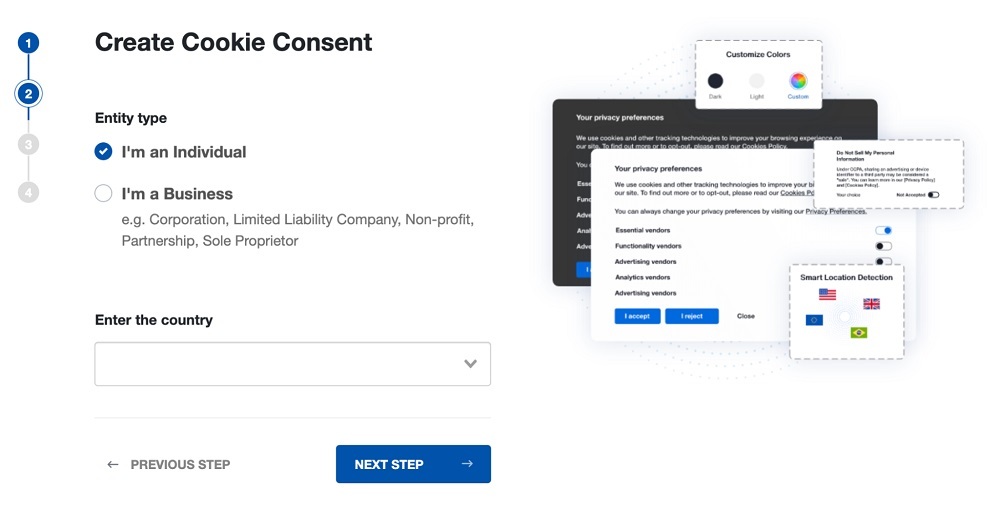
At Step 2, add in information about your business.
-
At Step 3, select a plan for the Cookie Consent.
-
You're done! Your Cookie Consent Banner is ready. Install the Cookie Consent banner on your website:
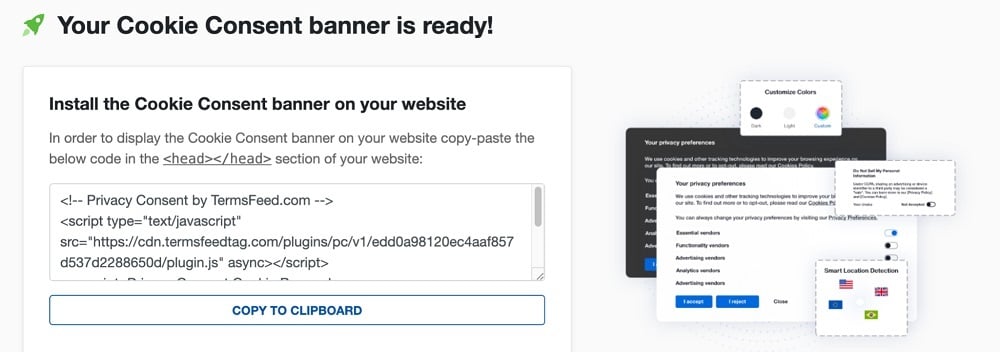
Display the Cookie Consent banner on your website by copy-paste the installation code in the
<head></head>section of your website. Instructions how to add in the code for specific platforms (WordPress, Shopify, Wix and more) are available on the Install page.


Show a Cookie Consent Banner on First Visit
Show the cookie banner on the first visit of users, before any non-essential cookie runs. A compliant banner needs to do the following.
- Appear before consent-based tracking begins: Users need to make their choice before any cookie or script requiring consent loads.
- Explain cookie purposes clearly: Use plain language so users understand which cookie categories the site uses and why before deciding.
- Give Accept and Reject comparable prominence: Refusing consent should require no more effort than accepting it. "Accept" and "Reject" buttons need equal visual prominence, and regulators treat asymmetric design as a dark pattern that invalidates consent.
- Offer granular choices: Users need separate controls for different purposes, such as analytics and marketing.
- Keep the site accessible: The site must remain accessible while the banner is shown, because blocking access until users accept all cookies creates a cookie wall.
You can place granular controls behind a Cookie Preferences option for users who want more detailed choices. The important point is that the first cookie banner layer still presents a meaningful way to accept or refuse non-essential cookies.
Block Non-Essential Cookies Before Consent
Technical blocking is the foundation of lawful consent. The default state of your website must restrict cookie deployment to essential cookies only. Non-essential cookies (like Google Analytics or retargeting tags) must be held in a blocked state until the user actively grants permission.
To automate this workflow, integrate a Consent Management Platform (CMP) or configure a tag manager (like Google Tag Manager) that gates relevant scripts and releases each script only after the visitor accepts the cookie category.
To test the gate, follow these steps.
- Open your website in an anonymous or private browsing window.
- Open the Developer Tools in your browser and go to the Network tab.
- Reload the page and verify that no third-party tracking or analytics requests fire before you click "Accept."
Let Users Manage and Withdraw Consent Anytime
Consent is an ongoing choice. Users must always be free to change their preferences at any time. To help them exercise this right under the GDPR and ePrivacy Directive, provide a permanent, easily accessible option or floating widget (such as a "Manage Cookies" link) in a prominent place like your website footer, as Invesco does below.

Your system must immediately stop loading non-essential cookies once a user withdraws their consent. In addition, only ask users for fresh consent if a material change occurs that falls outside their original choice. Examples include introducing new third-party trackers or updating your Cookie Policy.
List the Cookies You Use
To comply with the transparency requirements of the GDPR and ePrivacy Directive, you must maintain a comprehensive cookie inventory. While the law does not require you to provide a technical, itemized list of every single cookie name, it does require you to detail exactly what happens behind each consent choice.
To make your policy compliant and user-friendly, group your technologies into clear categories and record the following five details.
- Name: The identifier stored or accessed.
- Purpose: What the technology does.
- Provider: The organization responsible for it.
- Duration: How long it remains active or stored.
- Category: For example, strictly necessary, analytics, or marketing.
Below is an example of how this looks in practice for the standard Google Analytics cookie.
| Detail | Example |
| Name | _ga |
| Purpose | Distinguishes unique visitors to compile traffic reports |
| Provider | Google Analytics (Third-party) |
| Duration | 2 years |
| Category | Analytics / Performance |
Whether websites must list every individual cookie by name in a Cookie Policy is a common point of confusion. The GDPR itself does not address listing specific cookie names.
Regulatory guidance focuses on what users are told rather than on a fixed format. The UK Information Commissioner’s Office (ICO), for example, expects you to explain which technologies you use, what they are for, which third parties are involved, and how long each one lasts.
That said, some companies still choose to make a granular cookie inventory public to support their internal audits and broader transparency efforts. Below is how this approach looks in practice from the Fitbit Cookie List.

Regardless of whether you choose to display an itemized list or focus strictly on category descriptions, keeping your baseline cookie inventory updated is vital for maintaining a compliant privacy program.
Register and Store Consent Records
Store enough information to demonstrate what the user agreed to and how that consent was obtained. Article 7(1) of the GDPR places the burden on the controller to prove valid consent.
Regulators do not prescribe a single, fixed logging system. However, your evidence must be detailed enough to reconstruct the exact consent event, including the precise information and choices presented to the user at that time.
A reliable and legally robust consent log should record the following.
- The precise timestamp of the interaction
- A unique session or consent identifier
- The specific categories or purposes the user selected
- The exact method used to make the choice (e.g., a checkbox or button click)
- The specific version of the cookie banner and Cookie Policy displayed
There is no universal expiration date for keeping these records under the GDPR. You must retain this proof for as long as the underlying consent-based data processing continues.
Once that processing ends, retain the logs only for the duration required to meet legal obligations or to establish, exercise, or defend against legal claims. Collecting excessive personal data just to build a massive audit log works against the data minimization principle under the GDPR.
Do You Need a GDPR Cookies Policy?
Yes, if your website targets users in the EU or European Economic Area (EEA) and uses non-essential cookies, you must legally provide clear disclosures and obtain prior consent.
Article 5(3) of the ePrivacy Directive requires "clear and comprehensive information" about the purposes of storage or access before consent, while the GDPR adds transparency requirements where personal data is involved.
Common tracking technologies that trigger these legal obligations are as follows.
- Web analytics (e.g., Google Analytics)
- Behavioral advertising and remarketing pixels
- Social media plugins and widgets
EU privacy law does not strictly require a standalone document explicitly titled a "Cookies Policy." You can legally integrate your cookie disclosures directly into a general Privacy Policy. However, many businesses choose to publish a dedicated Cookies Policy to make the information accessible and user-friendly.
Cookies Policy vs. Cookie Notice
Businesses often conflate a Cookies Policy with a Cookies Notice, but they serve distinct compliance roles in data protection.
- Cookie Notice (The Consent Banner): The real-time user interface (banner or pop-up) that alerts visitors of cookies on their first visit to a website. It provides a short explanation and controls for accepting, rejecting, or managing cookies.
- Cookies Policy (The Legal Document): The standalone webpage detailing what cookies and similar technologies the site uses, their purposes, storage duration, relevant third-party data recipients, and explicit opt-out instructions.
You need both legal mechanisms if your website uses non-essential cookies. The notice handles consent events in real time, while the policy gives users relevant details to make an informed decision.
Cookies Policy vs. Privacy Policy (or Both?)
A Privacy Policy is mandatory under EU data protection law if you are processing the personal data of anyone in the EU. This includes using cookies.
Under Article 12 of the GDPR, you are required to provide information about all the personal data you process "in a concise, transparent, intelligible and easily accessible form, using clear and plain language."
While this means you need to provide information about cookies, you do not necessarily need a separate Cookies Policy for this. Simply include the information about cookies as a section in your main Privacy Policy. Oando, for example, combines its Privacy Policy and Cookies Policy into one comprehensive legal agreement.

Many companies do choose to present cookie information in a separate Cookies Policy, and this is a good solution. It keeps cookie details easier to find and update while the Privacy Policy covers the wider processing of personal data.
Just make sure you include a reference to your standalone Cookies Policy where relevant (most importantly, within your main Privacy Policy).
What to Include in a GDPR Cookies Policy
A complete Cookies Policy covers every facet of how your website stores and accesses cookies and similar trackers on visitor devices. While the ePrivacy Directive requires user consent before storing or accessing non-essential cookies, the GDPR sets the standard for what qualifies as valid consent.
To protect your business and respect user privacy, your Cookies Policy must provide the following key disclosures.
- What cookies are: Give a brief, plain-language explanation of cookies and similar tracking technologies like pixels and web beacons. A definition, such as "small text files a website stores on a device to remember information about a visit."
- Cookie categories and purposes: Explain the cookie categories you use, such as strictly necessary (exempt from consent), functionality, analytics, or marketing, and what each category does.
- Third-party cookies: Identify relevant third parties (like Google Analytics or Meta) that set or access cookies through your site and explain their role. Include links to their Privacy Policies where possible.
- Cookie duration: State how long cookies remain on the device. Distinguish between session cookies (temporary cookies that are deleted when the browser closes) and persistent cookies (cookies that remain on user devices for a set period).
- Consent controls: Provide step-by-step instructions on how users can freely accept, refuse, adjust their preferences, or withdraw their consent for non-essential cookies at any time.
- Cookie list: Where relevant, provide a clear table showing each cookie name, purpose, provider, duration, and category.
- Cookie management: Explain how users change preferences through your consent banner or mechanism and, where useful, through standard web browser settings.
- Policy updates: Explain how you notify users of material changes to your cookie usage to ensure your documentation always reflects your live website technology.
For cookies involving personal data, your policy must complete the transparency chain by explicitly stating the following.
- The specific legal basis for processing the data.
- The specific categories of recipients who will see the data.
- Clear instructions on how users exercise their GDPR rights, including the right to access, rectify, or erase their data, and, where relevant, how to contact your Data Protection Officer (DPO).
The Cookies Policy does not need to duplicate every disclosure already presented clearly in the Privacy Policy. Linking the two documents keeps broader personal-data information available while letting the Cookies Policy stay focused on tracking technologies and user choices.
How to Create a GDPR Cookies Policy
Follow these steps to write a Cookies Policy that reflects what your website does. The process starts with the technologies running on the site, then turns that technical inventory into clear disclosures and a working consent setup.
- Audit every cookie and tracking technology: Scan the site for cookies, pixels, local storage, analytics tags, advertising scripts, embedded services, and other trackers. Check more than the homepage. Login areas, checkout flows, videos, forms, and other interactions often introduce technologies that a basic scan misses.
- Categorize what you find: Group each cookie by its purpose, such as strictly necessary, preference, analytics, or marketing. Then identify which cookies require consent. Under the ePrivacy Directive, strictly necessary cookies are exempt from consent requirements because the site cannot function without them. All other categories generally require prior, explicit consent.
- Write the disclosures from the inventory: Use your audit inventory to document specific cookie names, their purposes, the data providers, cookie durations, and any involved third parties. Avoid copying technical descriptions from vendor dashboards. Instead, use plain, conversational language. Tailor these disclosures specifically to your website footprint rather than using vague, boilerplate cookie wording.
- Set up the policy and consent interface: Decide whether your cookie information will stay in a standalone Cookies Policy or as a clearly designated section within your Privacy Policy. Next, connect this policy to a Consent Management Platform (CMP) or cookie banner that lets users accept, refuse, and manage non-essential cookies by category.
- Publish, connect, and maintain the setup: Link your policy clearly within both your cookie banner and website footer, then configure the consent tool so trackers requiring consent remain blocked until the user opts in. Finally, establish a routine schedule to re-audit your site, as new plug-ins or marketing scripts introduce compliance risks.
For a head start on step 3, the GDPR Cookies Policy Template below provides ready-made wording to adapt.
GDPR Cookies Policy Template
This GDPR Cookie Policy template covers all essential compliance sections, including a clear explanation of what cookies are, a detailed breakdown of cookie categories, an overview of user consent rights, and easy instructions on how visitors change or withdraw their preferences at any time.
Replace the bracketed placeholders with the specific details of your business and privacy practices.
You can download the Sample Cookies Policy Template as HTML code below. Copy it from the box field below (right-click > Select All and then Copy-paste) and then paste it on your website pages.

Cookie Compliance Beyond the EU
Cookie consent isn't only a GDPR issue or an EU requirement. Achieving cookie compliance outside the EU requires navigating other international laws, as different countries enforce their own distinct cookie laws.
Because regulations vary significantly by jurisdiction, global cookie compliance depends on where your users are located and what each cookie does, rather than applying a single cookie banner configuration everywhere.
CCPA and CPRA Cookie Compliance
California takes a fundamentally different approach than Europe. While the GDPR requires explicit opt-in consent before non-essential trackers deploy, the California Consumer Privacy Act (CCPA), as amended by the California Privacy Rights Act (CPRA), operates primarily on an opt-out model.
However, California compliance involves distinct requirements.
- Notice at Collection: Businesses must inform users at or before the moment of collection about what data is being tracked and why.
- Cross-Context Behavioral Advertising: The CPRA specifically expanded consumer rights to cover the "sharing" of personal information for targeted, cross-context advertising. Third-party advertising trackers that pass user data to ad networks usually fall under this definition of sharing.
-
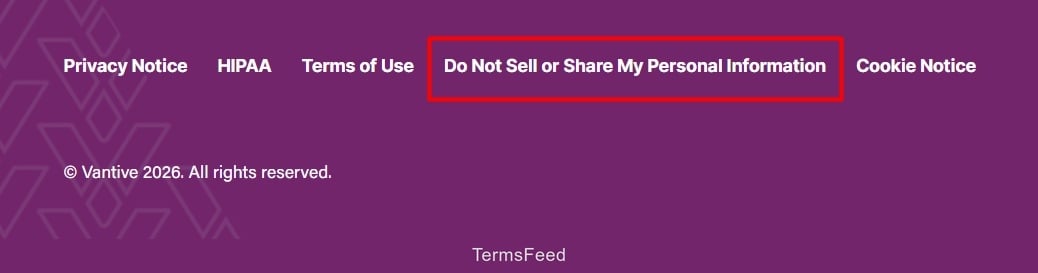
The Opt-Out Requirement: Covered businesses engaged in the "sale" or "sharing" of personal information must give California residents an easy way to stop it. This typically requires a clear "Do Not Sell or Share My Personal Information" link on the website. Below is an example of this link from Vantive in its website footer.
- Universal Opt-Out Signals: Businesses must automatically detect and honor frictionless opt-out preference signals sent by user browsers, such as the Global Privacy Control (GPC).

The core operational difference comes down to timing.
| Jurisdiction | Primary Mechanism | Data Collection Timing |
| European Union (GDPR) | Opt-In | Trackers must remain blocked until the user explicitly consents. |
| California (CCPA/CPRA) | Opt-Out | Data collection often begins immediately (provided a Notice at Collection is displayed), but users must be given the right to stop any qualifying sale or sharing. |
That said, not every advertising cookie automatically counts as a sale or sharing of personal information. The data flow and third-party relationship determine the result.
Other Cookie Laws (ePrivacy/PECR, PIPEDA, LGPD)
Other jurisdictions regulate cookies through different combinations of communications law, privacy law, consent rules, and advertising controls. Important examples include the following.
- UK PECR: The UK Privacy and Electronic Communications Regulations (PECR) largely mirror the ePrivacy Directive and require consent for non-essential cookies. However, under the Data (Use and Access) Act 2025, low-risk uses (such as statistical and functionality purposes) are exempt from prior consent, provided you offer a clear and free opt-out mechanism. Violations now match the UK GDPR fine threshold of up to £17.5 million or 4% of worldwide annual turnover.
- Canada PIPEDA: The Personal Information Protection and Electronic Documents Act (PIPEDA) requires meaningful consent to collect, use, and disclose personal information. The exact type of consent required depends on data sensitivity. Standard, non-sensitive behavioral advertising uses an opt-out model, but highly personalized or unexpected tracking requires explicit (opt-in) consent.
- Brazil LGPD: Brazil does not impose a universal cookie consent rule. Instead, the National Data Protection Authority (ANPD) differentiates by cookie purpose. Essential cookies (e.g., shopping carts) do not require consent, but non-essential cookies (like tracking pixels) need user consent. Businesses must provide distinct cookie categories and a clear, single-click option to reject non-necessary cookies.
- Australia Privacy Act: The Privacy Act 1988 has no cookie-specific consent rule, but cookie data that identifies a person counts as personal information, which requires clear notice. The Office of the Australian Information Commissioner (OAIC) requires transparency and a simple opt-out for targeted advertising. That said, sensitive data (such as health or biometric information) gathered via cookies requires prior express consent.
For businesses serving several regions, the safest operational approach is to map each tracker to its purpose and data flow, then apply the rules that govern user location rather than assuming a GDPR-style banner satisfies every cookie law.
Remember that the proposed ePrivacy Regulation intended to replace the ePrivacy Directive was withdrawn in 2025, so businesses still need to follow the directive through relevant EU national laws.
Google Consent Mode and GDPR Cookies
If you use Google Analytics or Google Ads, Consent Mode matters because it decides how these tracking tools behave for visitors from the European Economic Area (EEA) and the UK.
Google Consent Mode v2 (the latest version) communicates visitor privacy choices to Google tags using seven distinct consent signals, which include the four core advertising and analytics parameters alongside functionality, personalization, and security storage types.

Since March 2024, Google has required these signals for all EEA traffic. Without them, core measurement, audience building, and remarketing features will fail to function.
Google tags function normally when a visitor accepts cookies, but if the visitor refuses, the tags switch to a restricted "cookieless" mode, and Google fills the data gap with behavioral modeling based on visitors who consented.
Consent Mode runs in 2 versions, and their differences matter significantly for GDPR compliance.
- Basic Consent Mode (Higher Legal Safety): Google tags remain completely blocked until the user interacts with your cookie banner. No data or pings are sent to Google beforehand. The tags remain blocked, and no data is shared if the user refuses consent.
- Advanced Consent Mode (Higher Data Volume, Higher Legal Risk): Google tags load once when a page opens, defaulting to a "denied" status. Before the user interacts with the banner, the tags send "cookieless pings" to Google. While these pings do not read or write cookies, they still transmit network information like IP addresses. The tags upgrade to full tracking only if the user grants consent.
Keep in mind that Consent Mode is not a cookie consent banner and cannot replace a valid mechanism for obtaining user consent. A Consent Management Platform (CMP) or custom banner must first legally collect the user choices. Consent Mode then communicates those choices to Google.
Businesses typically implement Consent Mode v2 using a Google-certified CMP or via Google Tag Manager (GTM). This setup ensures that "denied" defaults are established before any Google tags fire, and are dynamically updated the moment a user makes their choice.
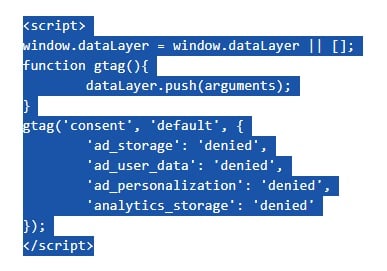
In November 2023, Google released Consent Mode V2, a new way for businesses to communicate EEA and UK users' consent choices regarding the use of their personal data for advertising purposes to Google.
To comply with the new requirement, you'll need to implement Consent Mode V2 by March 2024. We've updated our Free Cookie Consent to work with Google Consent Mode V2.
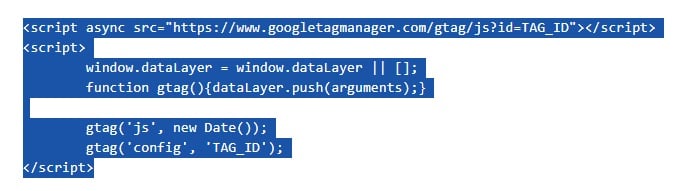
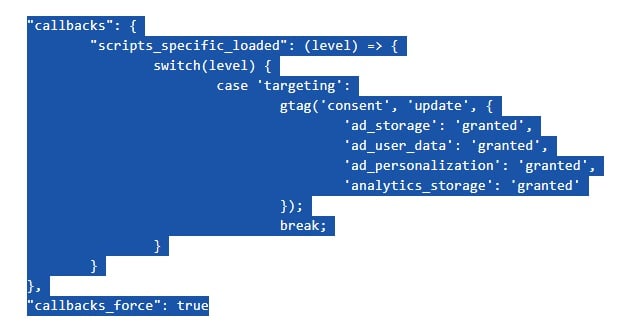
Here's how you can integrate our Free Cookie Consent with the new Consent Mode V2:
-
Create the gtag function with the default consent states as denied:
-
Load the Google Analytics/Tag Manager script:
-
Communicate user consent status using Cookie Consent callbacks:


These instructions can be found on our Cookie Consent & Google Consent Mode V2 page. We also have a video walkthrough on how to integrate a cookie notice banner with Consent Mode V2.
How to Audit Your Cookies for GDPR Compliance
Use this printable, step-by-step checklist to make sure your Cookies Policy meets the requirements of the GDPR and ePrivacy Directive:
☐ Scan your website with a cookie scanner or browser DevTools to identify cookies, pixels, tags, and similar technologies
☐ Record the name, purpose, provider, duration, and category of all cookies and trackers
☐ Identify every third-party vendor that sets or accesses cookies through your site
☐ Classify each tracker as “strictly necessary” or “consent-required” based on its actual purpose
☐ Test the site before accepting cookies and flag any consent-required tracker that loads too early
☐ Update your Cookies Policy and cookie list (if applicable) so they match the cookies and similar technologies found during the audit
☐ Re-scan the site regularly and after adding or changing plugins, analytics tools, advertising platforms, or embedded services

GDPR Cookie Consent Fines and Penalties
The maximum GDPR fines reach up to €20 million or 4% of worldwide annual turnover from the preceding financial year, whichever is higher. Article 83(5)(a) of the GDPR explicitly categorizes violations of data processing consent conditions under this maximum penalty tier.
Article 15a of the ePrivacy Directive leaves EU Member States responsible for setting penalties for breaches of their national cookie rules. Fines and enforcement procedures therefore differ across the EU.
Recent enforcement shows the range.
| Regulator | Company | Year | Amount | Issue |
| CNIL (France) | Google LLC & Google Ireland | 2025 | €325 million | Placing cookies during account sign-up without clear information, and serving ads directly inside Gmail accounts without prior consent. |
| AEPD (Spain) | Vueling Airlines | 2019 | €30,000 (later reduced to €18,000) | Operating a restrictive cookie banner that gave users no structural way to reject cookies. |
| CNIL (France) | Microsoft Ireland | 2022 | €60 million | Rejecting cookies was not as easy as accepting them |
| Dutch DPA (The Netherlands) | Coolblue | 2024 | €40,000 | Using tracking cookies via "default consent" architecture, including unprompted tracking and pre-ticked consent checkboxes. |
| CNIL (France) | Criteo | 2023 | €40 million | Failing to verify and prove that users had consented to its tracking cookie, which partner websites were responsible for collecting. |
Almost every case above traces back to 2 key failures.
- Deploying cookies onto user devices before they actively click "Accept."
- Using dark patterns that make refusing cookies significantly more difficult or time-consuming than accepting them.
A compliant, user-friendly cookie banner prevents both, and maintaining a detailed consent record helps you prove compliance when a regulator asks. For a more comprehensive breakdown of the GDPR penalty system, check out our article: GDPR Fines.
GDPR Cookies Policy: Frequently Asked Questions
Here are answers to common questions about GDPR Cookies Policy requirements.
Yes, if your website targets EU users and uses cookies or trackers that require consent, you need to provide clear information about them. EU law does not require a document with the exact title "Cookies Policy,” so the disclosures may appear in a standalone policy or a clearly separated part of a Privacy Policy.
Yes. EU law focuses on whether users receive clear, accessible information rather than requiring separate documents. That said, a standalone Cookies Policy often keeps detailed cookie tables and consent instructions easier to find and update.
Google Consent Mode is a framework that tells Google tags how to behave based on the consent choices made by a user. Basic Consent Mode blocks Google tags before consent, while Advanced Consent Mode permits limited cookieless measurements under denied consent states. Consent Mode does not collect valid consent itself, so it works alongside a consent banner or CMP.
Summary and Key Takeaways
A compliant GDPR Cookies Policy starts with knowing what your site tracks and giving users meaningful control. Below are the key points to remember when creating your GDPR Cookies Policy.
- Get valid consent before any non-essential cookie or tracking technology loads or accesses information on user devices.
- Treat consent as valid only where it is freely given, specific, informed, affirmative, easy to withdraw, and supported by records that demonstrate the choice.
- Exempt only cookies and technologies that meet the narrow strictly necessary test for providing a service the user explicitly requested.
- Make your Cookies Policy clear about cookie categories, purposes, third parties, durations, consent controls, and the technologies currently in use.
- Account for regional differences, including the GDPR opt-in model and CCPA/CPRA opt-out rights for qualifying sales or sharing of personal information.
- Audit your cookies regularly so your Cookies Policy, consent banner, and live tracking setup stay aligned as tools and scripts change.
- Use Google Consent Mode alongside a properly configured consent system where Google Analytics, Google Ads, or related Google tags form part of your tracking setup.
Creating and maintaining a Cookies Policy manually is often tedious and prone to error, especially as your website changes. The TermsFeed Cookies Policy Generator helps you create a tailored, attorney-reviewed policy in minutes through a guided questionnaire, so your business provides compliant disclosures without hassle.

The first step to compliance: A Privacy Policy.
Stay compliant with our agreements, policies, and consent banners — everything you need, all in one place.


